infographic · chapter · graph · drafted
Who can read what
For ch. 24, Privacy by design: SG/Send, sgit, and the value of constraints · proposal who-can-read-what-sgit in the plan
The SVG The data Review it in the plan
What it is for
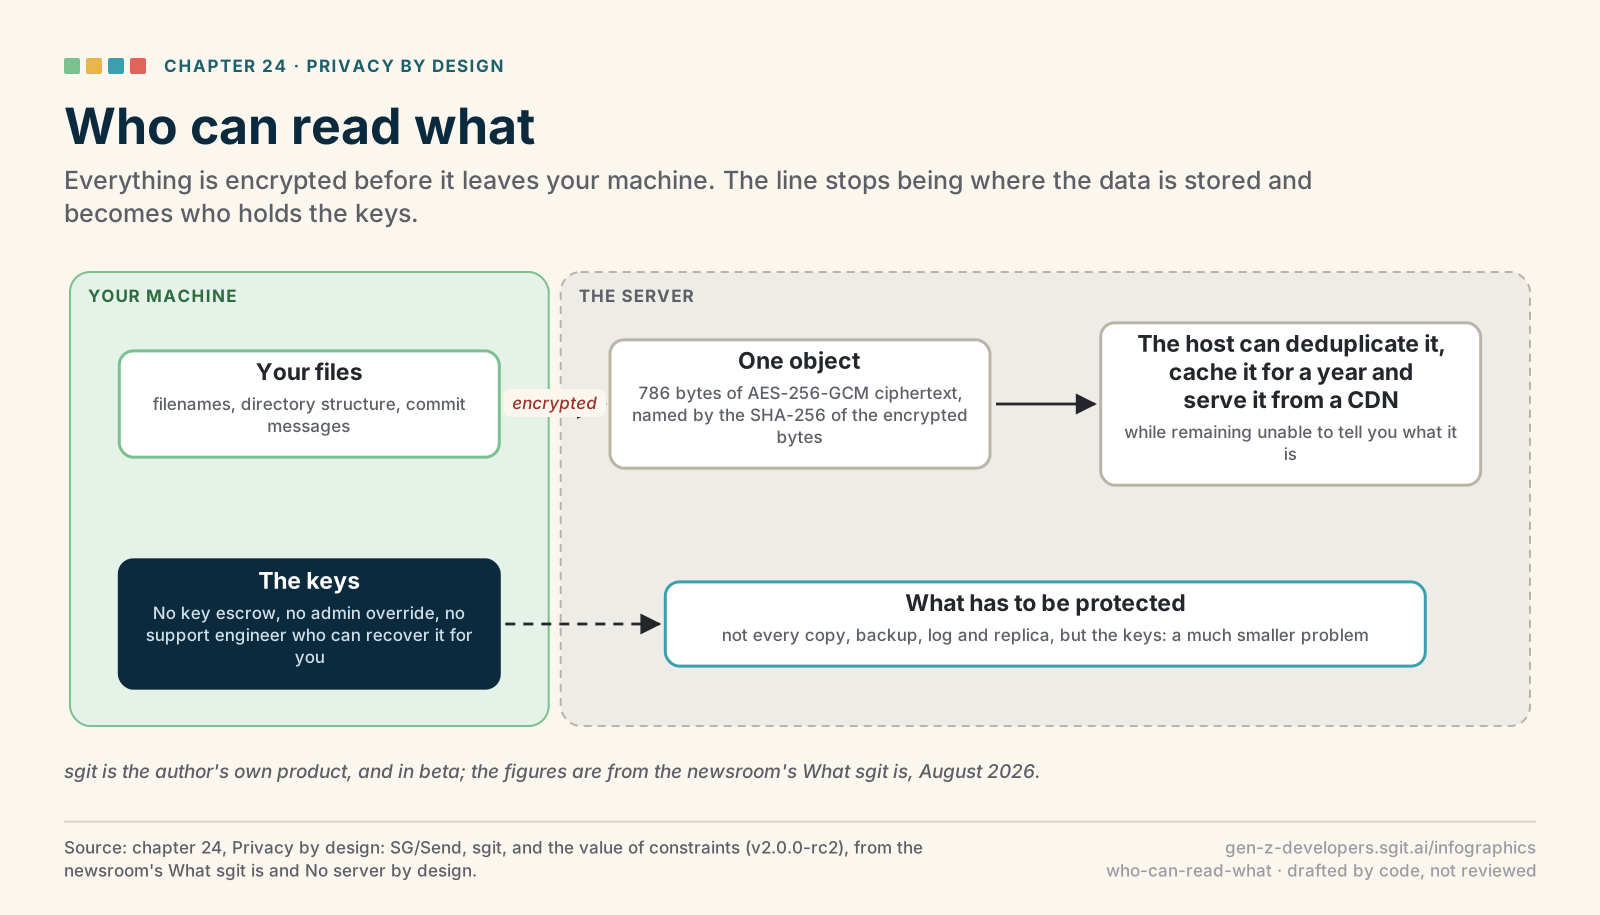
Answers the non-coder's first question about part 7, where the data lives and who can read it, and shows why the problem moves to the keys.
How it is made
Drawn by admin/build/infographic_svg.py from admin/content/infographics/drawn/who-can-read-what.json, as a graph. Change the data and rebuild; the picture follows. It keeps the book's colours in every theme of this site, because it is a printed picture: the same file goes into the PDF.
Notes
sgit is beta; the infographic should not imply more. Numbers (786 bytes) from the August 2026 article.
Checked against the source
Every line below is on the drawing or behind it, and the build found each one word for word in v2/content/7-build-it-without-a-server/24__privacy-by-design.md. A line changed in the chapter and not here stops the release.
- “Everything is encrypted before it leaves your machine” ✓
- “The line stops being where the data is stored and becomes who holds the keys.” ✓
- “not your filenames, not your directory structure, not your commit messages” ✓
- “no key escrow, no admin override and no support engineer who can recover it for you” ✓
- “786 bytes of AES-256-GCM ciphertext, named by the SHA-256 of the encrypted bytes” ✓
- “the host can deduplicate it, cache it for a year and serve it from a CDN while remaining unable to tell you what it is” ✓
- “every copy, backup, log and replica” ✓
- “the problem moves to protecting the keys, which is a much smaller problem” ✓